Your judgment, in the workflow.
Review proposed detections and containment actions before they run. Define which other actions policy can authorize.
The cybersecurity operating system
Your tools see the signals. Corticle connects the context, carries the work forward, and keeps your people in command.
Your existing tools.
One connected security program.
Different jobs. The same layer.
The hardest part of security shouldn’t be the handoff.
The SOC has the alert. Compliance needs the evidence. Leadership wants to know what changed. Too often, your people have to connect it all by hand.
Corticle carries that context across the program, over the tools you already own, so the next team starts with what the last team already knows.
02 / Over the stack you already own
Corticle is the operating layer on top of the tools you already run. Where the stack covers a job, Corticle works over that tool. Where you have a gap, it fills the capability. The data stays where it lives.
CISO · SOC Analyst · Detection Engineer · Incident Responder · Blue Team · Red Team · IAM Manager · Risk Analyst · Assessment Lead · GRC Officer · Compliance Officer · TPRM Manager · Training Manager · Security Architect · CTI Analyst · Platform Admin
queried in place — no data movement, no new data lake
SIEM · EDR · Vuln Mgmt · ITSM · IAM · Cloud (AWS / Azure / GCP) · GRC · Threat Intel · Training · Email Sec · WAF · SBOM · CMDB · NDR
deploys on-prem · in your cloud · air-gapped. See workflows for a few of these jobs → · The platform in depth →
03 / Built around your authority
Specialized agents work across your security program, guided by your policies and the context of your environment.
Explore our trust approachReview proposed detections and containment actions before they run. Define which other actions policy can authorize.
Trace decisions back to their evidence, approvals, and outcomes through an append-only, hash-chained audit log.
Work with your existing tools and data, with deployment options for your cloud, on premises, and air-gapped environments.
What changes
From weeks to minutes.
triage · attestations · assessments
From quarterly to continuous.
audit · risk · vendor · posture
From scattered to one screen.
every domain · every role · one program
From months of integration to days.
patent-pending auto-integration
Engineered against — SOC 2 · HIPAA · CMMC · FedRAMP · NIST CSF · PCI DSS · ISO 27001 · CJIS · IRAP · StateRAMP. Our own certifications are in progress. Trust posture →
04 / Why we built Corticle
Jesse had described a future for cybersecurity on a conference stage. Years later, after their time at Amtrak, Mac came back to that idea with a question:
“Do you want to build it now?”
That conversation became Corticle. Together with Alex, they’re building from experience in operations, engineering, and governance — connecting the work they once had to hold together by hand.
From Jesse’s account of Corticle’s beginnings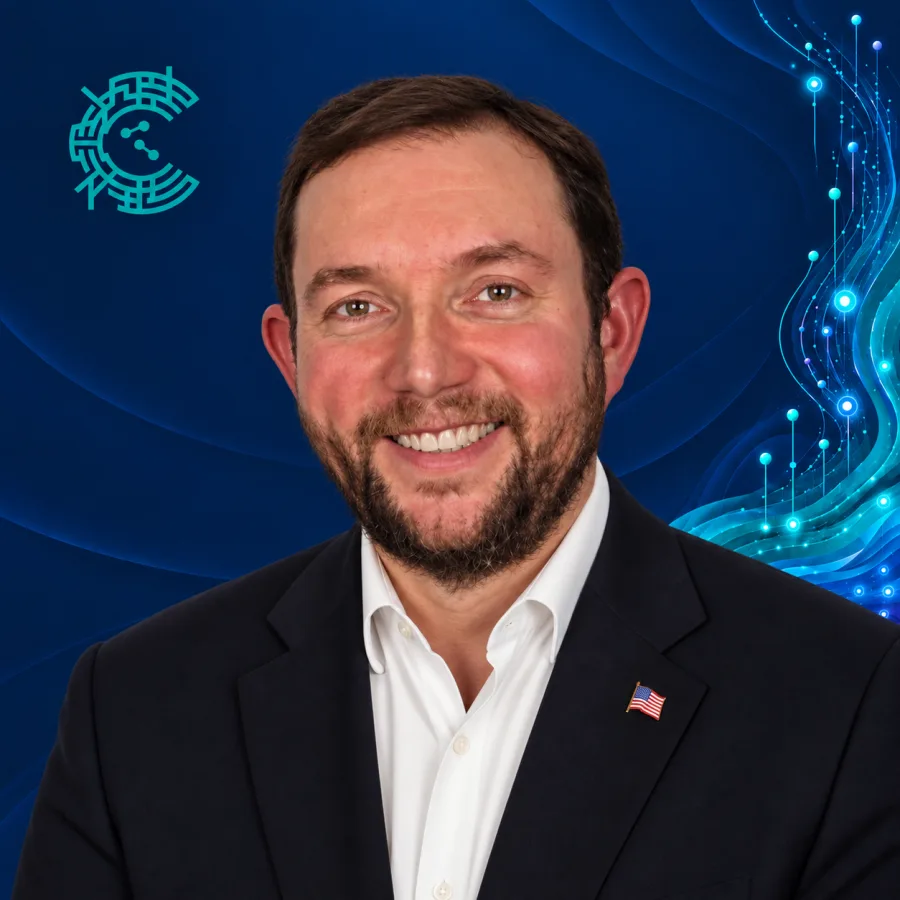 LEADERSHIP
CEO & co-founder
Former Amtrak CISO and Pentagon cybersecurity operations leader. 2024 Capital ORBIE CISO of the Year. U.S. Army veteran.
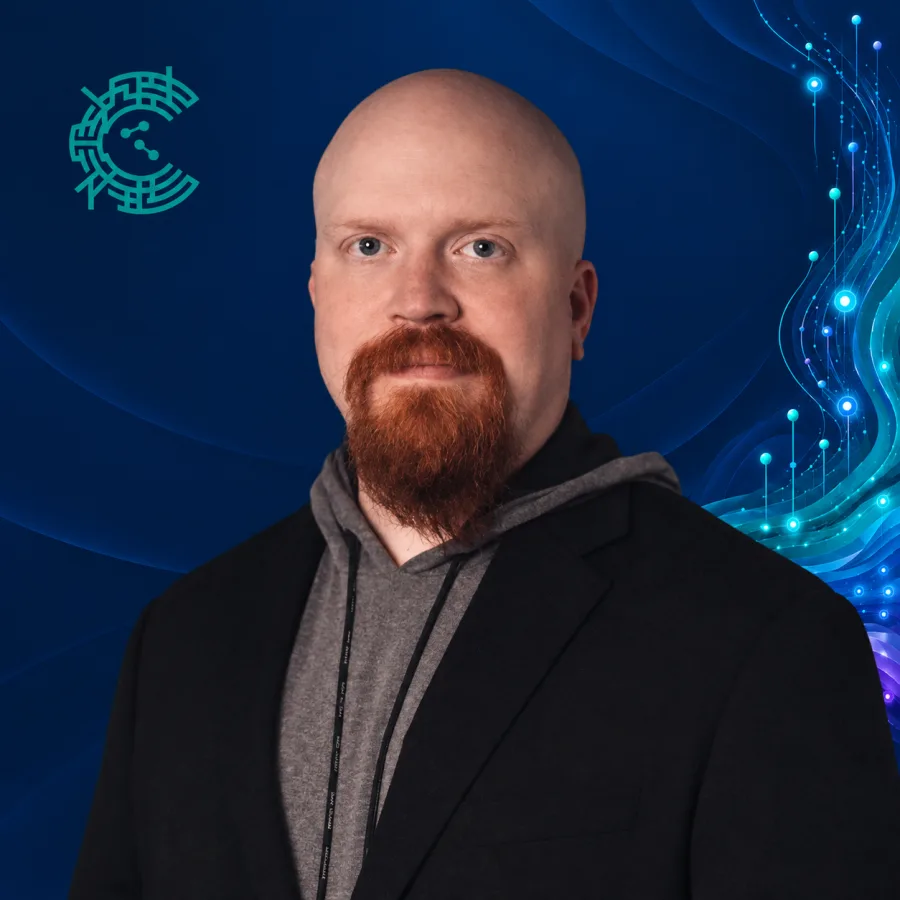 ENGINEERING
CTO & co-founder
Former Amtrak security technology leader. Eight years at NSA Tailored Access Operations. U.S. Marine veteran.
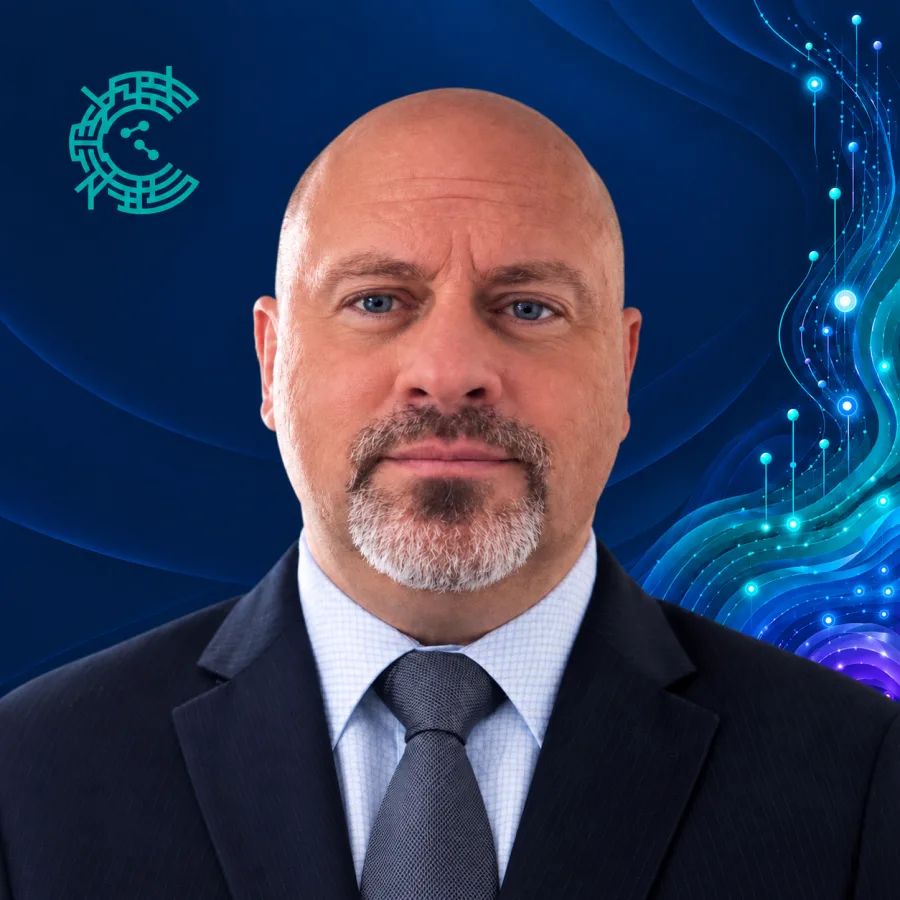 GOVERNANCE
CISO & co-founder
Security governance and risk leadership at Amtrak and Thermo Fisher Scientific. U.S. Navy veteran.
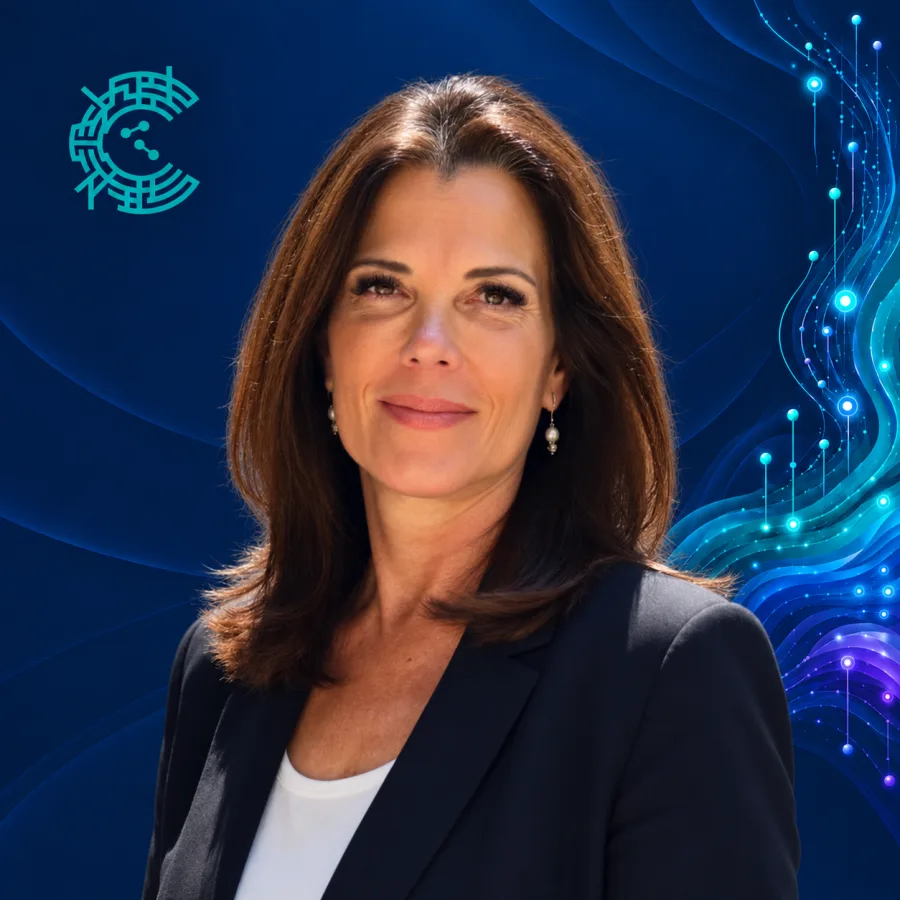 REVENUE
Chief Revenue Officer
Led Government Solutions for DataBee and BluVector at Comcast. Twenty-five years taking security technology to market across DoD and the Fortune 500.
Let’s connect the picture.
We’ll walk through how Corticle connects the people, context, and decisions on either side.